Mozambique Takes Cybersecurity Policy to Its Regions
Mozambique is writing its cybersecurity strategy for 2026 to 2030, and it is asking the provinces, not just the capital. Whether their voices shape the final document is the real test.
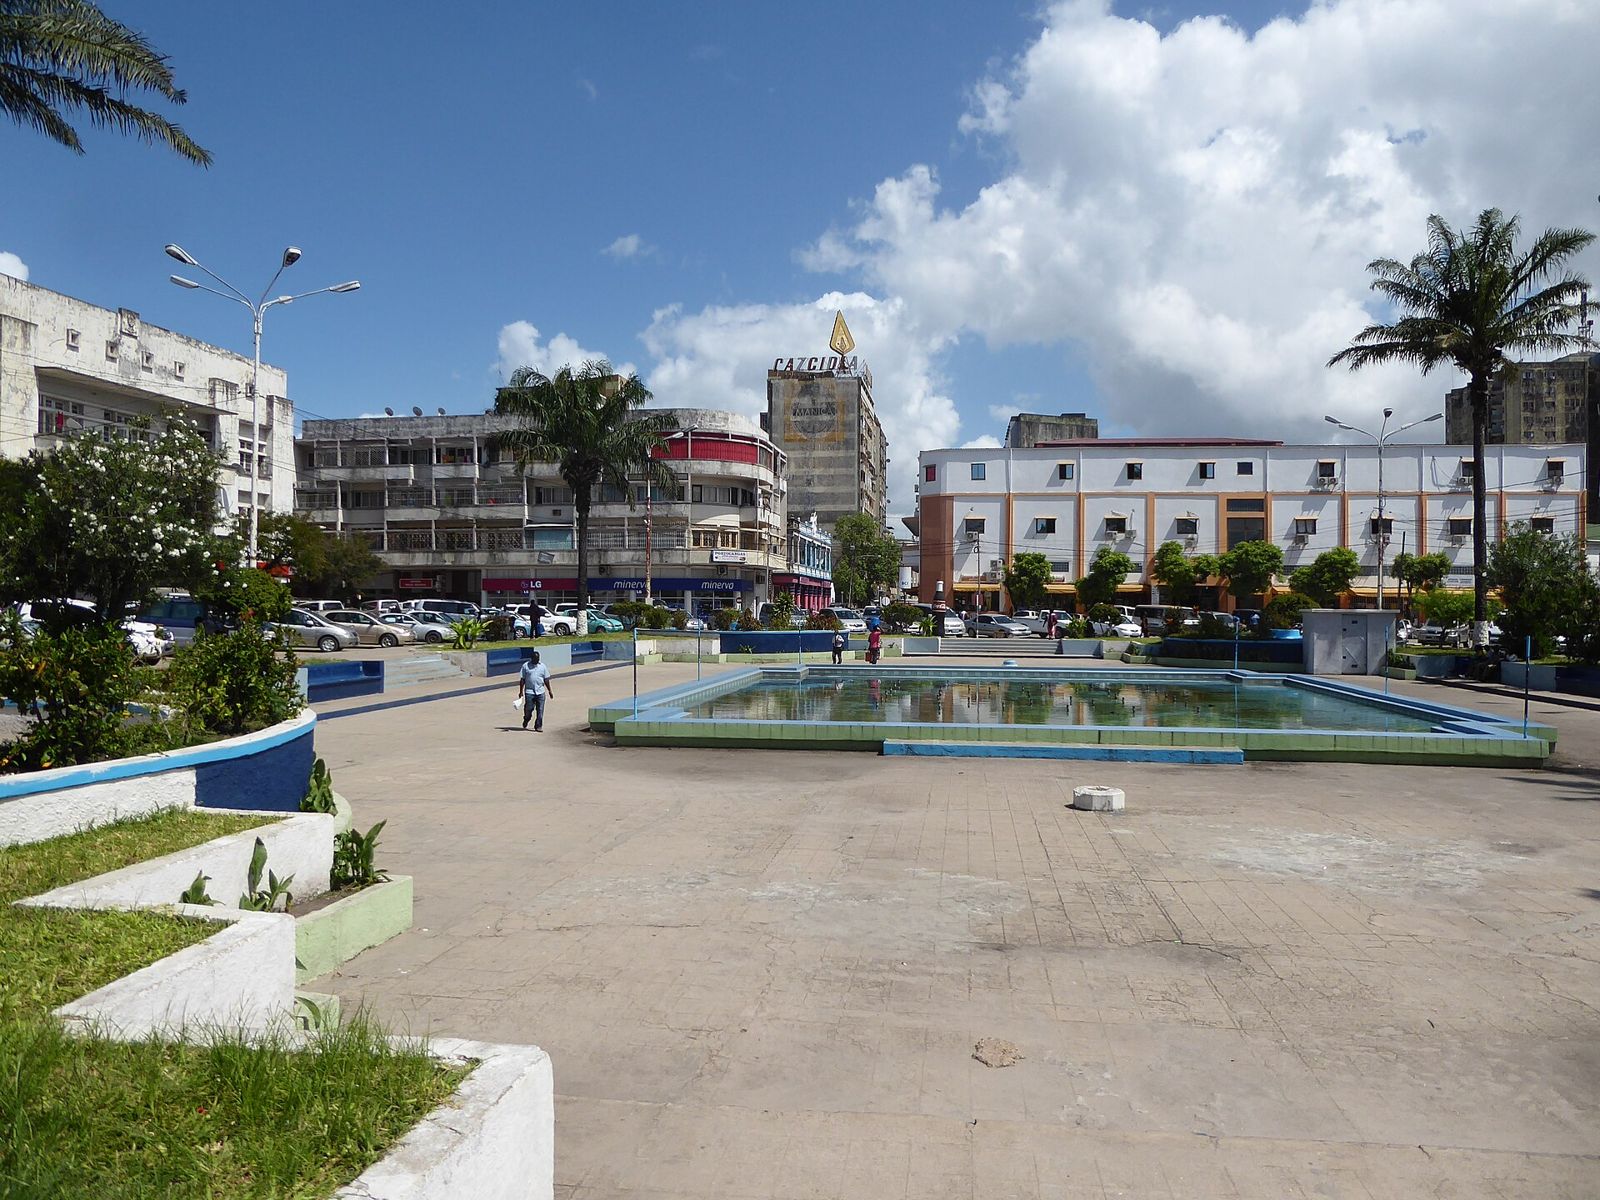
Praça do Município, Beira. Photo: Cornelius Kibelka, via Wikimedia Commons, CC BY-SA 2.0 (licence)
On 6 October 2026, government officials, cybersecurity specialists and regional stakeholders gathered in Beira, a coastal city in Mozambique's Sofala Province. The subject was the country's next National Cybersecurity Strategy, a document intended to guide how Mozambique protects its digital infrastructure, public services, businesses and citizens through to 2030.1
It might sound like an ordinary government consultation. National strategies are regularly developed through meetings involving ministries, technical experts and international advisers. What makes Mozambique's current approach interesting, however, is where those conversations are taking place.
Rather than concentrating the entire process in the capital, Maputo, Mozambique's National Institute of Information and Communication Technologies (INTIC) has been holding consultations in different parts of the country. The aim is to understand the cybersecurity challenges experienced by institutions and businesses operating under different regional conditions, and to bring those perspectives into the development of national policy.
The consultation in Beira was one part of a wider exercise. According to INTIC, meetings have taken place in Maputo, Inhambane, Nampula, Tete, Sofala and Gaza, involving representatives from government institutions, businesses, universities and civil society organisations.2
It reflects an important question in national cybersecurity planning. A strategy may establish priorities for an entire country, but the institutions expected to implement those priorities do not necessarily have the same resources, infrastructure or operational requirements.
For Mozambique, recognising those differences is becoming part of how its next strategy is being developed.
The country's National Cybersecurity Strategy 2026–2030 is intended to build on an earlier framework covering 2021 to 2025. That previous strategy addressed national cyber resilience, protection of critical information infrastructure, legal and institutional arrangements, and the development of a stronger cybersecurity culture.
The new process is examining what has been achieved, where improvements are still needed and how the country should respond to developments in its digital environment.
As Mozambique expands its use of digital public services, communications infrastructure and technology across the economy, protecting those systems becomes increasingly important. A disruption affecting government information systems can interfere with public administration, while an incident involving a telecommunications provider or financial service can create difficulties for businesses and customers.
However, the consequences of cybersecurity incidents are not necessarily experienced in the same way everywhere.
A public institution in Maputo may have access to specialist technical staff and established relationships with national authorities. An organisation operating in another province may face different conditions concerning connectivity, equipment, financial resources or access to cybersecurity expertise.
These are considerations that can influence how national standards are implemented in practice.
A policy requiring organisations to introduce particular security controls, for example, needs to account for the capabilities of those responsible for maintaining them. Similarly, national incident-reporting arrangements must be accessible to institutions operating outside major administrative centres.
This does not mean that Mozambique's provinces necessarily require entirely different cybersecurity policies. It means that understanding the circumstances in which a common national policy will operate is an important part of developing one.
That was the purpose of the Beira consultation.
INTIC's Cybersecurity Division Director, Eugénio Jeremias, attended alongside consultants from the country's National Computer Security Incident Response Team and Finnish technical adviser Perttu Luhtakanta.1
Participants discussed the prevention and detection of cyber incidents, response arrangements and the ability of organisations to recover when attacks or failures affect digital services.
The emphasis on recovery is particularly relevant. Cybersecurity is often discussed in terms of preventing unauthorised access or identifying malicious activity, but organisations also need to maintain essential functions when preventive measures are unsuccessful.
For businesses, that can involve restoring access to customer information, continuing transactions or maintaining communication with suppliers. For public institutions, it may mean ensuring that citizens can continue accessing important services.
The capacity to recover is influenced by technical systems, staff expertise and operational planning, all of which can vary between organisations and regions.
Mozambique's regional consultations provide an opportunity for these practical considerations to be raised before the new national strategy is finalised.
The approach is not entirely new in cybersecurity policy. Governments elsewhere also conduct stakeholder consultations when developing national strategies. What stands out in Mozambique's current process is the documented effort to extend participation across multiple provinces and involve organisations beyond central government.
In Nampula, for example, approximately 40 participants from the public sector, private businesses, universities and civil society attended a consultation in May 2026. Held at the Catholic University of Mozambique, the meeting contributed to the assessment of the previous cybersecurity strategy and the preparation of its successor.3
Further consultations followed in other provinces, including Gaza on 1 October and Sofala on 6 October.4,1
The process gives Mozambique's regional institutions an opportunity to communicate concerns that might not otherwise receive the same attention in national policy discussions.
For a business operating outside Maputo, those concerns could include access to trained cybersecurity personnel, the cost of implementing protective measures or the reliability of the digital services on which its operations depend.
Universities may have different priorities, including cybersecurity education, technical research and the development of locally available expertise.
Civil society organisations can contribute perspectives concerning digital literacy, access to secure communications and the implications of cybersecurity measures for the people using online services.
These are examples of the kinds of issues regional consultation can help identify. The published accounts of the meetings do not yet provide a comprehensive record of every concern raised by participants or how individual contributions will be reflected in the final strategy.
That distinction matters. Inviting organisations into a consultation creates an opportunity for participation, but it does not automatically establish that those organisations will influence the final decisions.
The more important test will come when the strategy is published and its priorities, funding arrangements and implementation responsibilities become clear.
There is already some evidence of the practical issues being discussed.
During a technical meeting in September, participants considered proposals to strengthen the protection of critical information infrastructure, expand specialist training and develop cybersecurity technologies suited to Mozambique's needs.
Recommendations included stronger partnerships with universities to support research, innovation and the development of technical capabilities within the country.
Participants also called for clearer implementation deadlines and financing arrangements, recognising that a national strategy requires more than a list of objectives if it is to produce measurable changes.5
These discussions connect the regional consultation process with a broader question facing developing cybersecurity ecosystems: how to translate national ambitions into capabilities that institutions can actually maintain.
Mozambique is not beginning that work from nothing.
INTIC reports that the previous 2021–2025 strategy contributed to the establishment of a national Computer Security Incident Response Team, the development of a network of sectoral response teams and the creation of a National Cybersecurity Observatory.
The country has also conducted national cybersecurity simulation exercises intended to strengthen preparedness and coordination.2
The legal framework has moved too. On 1 July 2026, Mozambique published a Cybersecurity Law (Law No. 13/2026) and a Cybercrime Law (Law No. 14/2026). The cybersecurity law creates a National Cybersecurity Council chaired by the Prime Minister, makes reporting of significant incidents mandatory and sets minimum security requirements for the organisations it covers.6,7
These developments provide an institutional foundation for the new strategy. However, maintaining and extending such capabilities requires continuing investment in technical expertise, cooperation and operational resources.
The development of a national response structure is particularly important where cybersecurity incidents may affect organisations with limited capacity to investigate attacks independently.
A smaller institution may not have a dedicated team capable of analysing malicious software or investigating compromised systems. Access to national or sectoral incident-response expertise can therefore provide support that would otherwise be difficult to obtain.
The proposed strategy aims to strengthen these arrangements while improving coordination between institutions.
An international dimension is also present.
Finland has been providing technical assistance to Mozambique through the Finnish Digital and Green Transition project, financed by the Finnish Ministry for Foreign Affairs.
The cooperation has supported the strategy's development, including expert assistance and funding for stakeholder consultations.
According to INTIC, Finland provided two specialists and financial support that helped enable the six consultation sessions held across Mozambique.2
The involvement of Finland is relevant because it introduces international experience into a process concerned with Mozambique's own national requirements.
During the September technical discussions, Finnish adviser Perttu Luhtakanta referred to Finland's comprehensive security approach, which treats the protection of essential national functions as a responsibility shared between public institutions, businesses and wider society.
The principle has relevance for cybersecurity, where critical services frequently depend on systems owned or operated by different organisations.
However, the involvement of Finnish experts should not be understood as Mozambique simply adopting Finland's cybersecurity model.
The regional consultation process is explicitly intended to identify Mozambique's own needs and incorporate them into the proposed national framework.
The challenge is to make international technical experience useful within the country's institutional, economic and regional circumstances.
That includes recognising that different organisations may have different levels of resources and that implementing common security objectives can require different forms of support.
The commercial implications are also worth examining.
For Mozambique's businesses, cybersecurity is increasingly connected to the reliability of payment services, telecommunications, digital records and online operations.
A company investing in new technology needs confidence that it can protect customer information and maintain its services. Businesses providing technology to government institutions may also need to meet increasingly defined security requirements.
The development of national cybersecurity capabilities can create opportunities for local technical specialists, training providers and companies offering security services.
Partnerships between universities, government institutions and businesses could also contribute to professional training and the availability of expertise within Mozambique.
However, the extent of those opportunities will depend on the final strategy and the resources allocated to implementation. The consultation announcements do not establish specific future investment commitments or guaranteed commercial outcomes.
The stakes extend beyond business.
Public institutions increasingly use digital systems to deliver services and manage information. Citizens rely on these systems for activities that may include communication, public administration and access to financial services.
Ensuring that those services remain available and that personal information is adequately protected is part of the wider purpose of national cybersecurity policy.
INTIC has also reported a developing threat environment. During a September cybersecurity event, the institute identified fraud, phishing, social engineering, ransomware and malicious software among the threats affecting Mozambique.
Data presented by the national incident-response team recorded 5,654 detections of attempted ransomware infection between January and July 2026. These were detections of attempted infection, not a count of confirmed successful attacks.5,7
The figures provide some context for why national institutions are seeking to improve prevention, detection and response capabilities.
Yet cybersecurity risks are only one part of the question. Governments also need to understand whether the organisations responsible for protecting systems have the resources and knowledge necessary to do so.
This is where the regional consultations may become particularly significant.
A national policy can establish what institutions should achieve, but discussions with those institutions can reveal obstacles to implementation that are not always visible from central government.
For Mozambique, that includes understanding how organisations operate across different regions, what support they require and how national cybersecurity responsibilities can be coordinated across public and private sectors.
The current strategy development process recognises these issues by bringing a wider range of participants into the conversation.
Whether that participation translates into meaningful influence will become clearer as the National Cybersecurity Strategy 2026–2030 moves from consultation to approval and implementation.
As of October 2026, INTIC describes the document as being in a preliminary stage, with contributions still being collected and consolidated. Its stated objectives include strengthening national resilience, protecting citizens and information, improving incident response and ensuring the continuity of essential services.
Those objectives are familiar within national cybersecurity policy. The more interesting development is the effort to understand them through the experiences of institutions operating in different parts of Mozambique.
National cybersecurity strategies are often judged by their ambitions, the legislation supporting them or the technical capabilities they seek to establish.
Mozambique's consultation process raises another consideration: how well a national policy reflects the circumstances of the organisations expected to put it into practice.
The meetings in Beira, Nampula, Gaza and other provinces do not yet demonstrate that Mozambique has resolved the difficulties of developing a national cybersecurity system. Nor do they guarantee that the final strategy will incorporate every regional concern.
They do show that the government is seeking input beyond the institutions normally associated with national cybersecurity planning.
For a country working to strengthen its digital services, businesses and public institutions, that provides a broader foundation for discussing what effective cybersecurity should look like.
The next stage will be determining how the contributions gathered across Mozambique influence the final document, and whether the resulting commitments are supported by the resources and responsibilities needed for implementation.
For now, the story is not simply that Mozambique is writing another cybersecurity strategy. It is that the country has taken part of the process into its provinces, asking institutions beyond the capital to contribute to the priorities intended to guide national cybersecurity through 2030.
Corrections: none. If you spot an error, tell us and we will correct it openly.